Velocity is the defining risk of the AI era.
Is your audit team equipped for the speed of risk?
Now it can be. CoAuditor pairs your auditors with MJ, an AI agent that does the manual work, so your people can focus on judgment.
 SOC 2 Type II attested
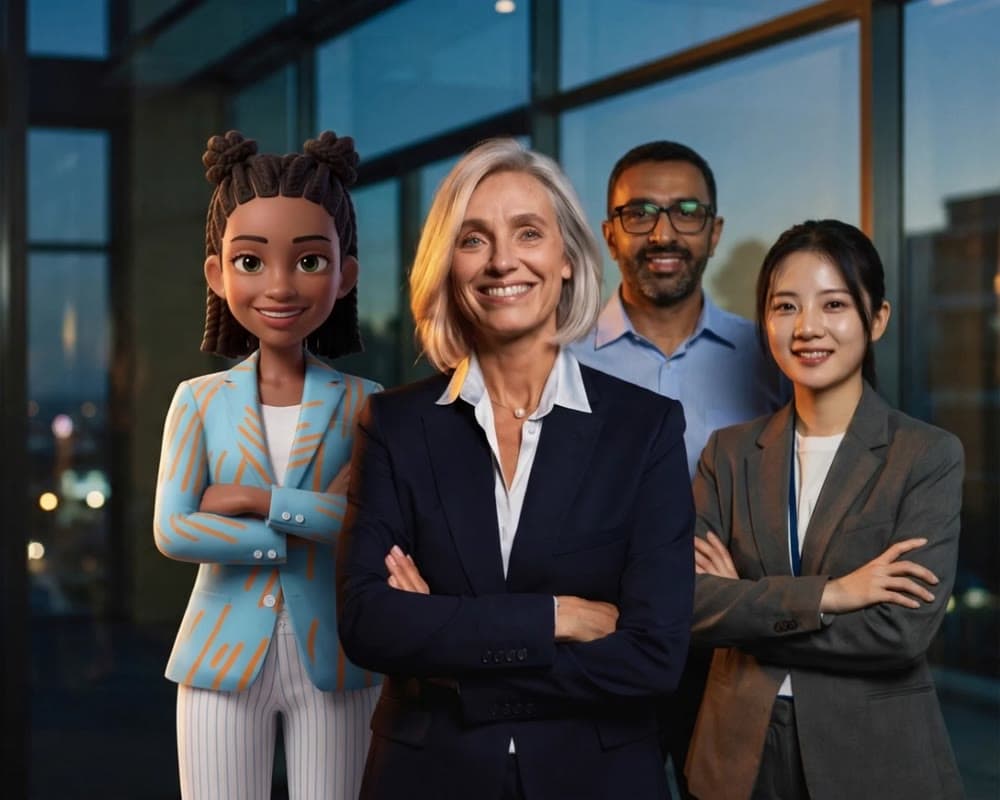
MJ takes the manual work. Your team does what humans do best.
MJ handles the manual and admin tasks across the audit, so your auditors spend their time on judgment, relationships and the business.
MJ, the AI agent in CoAuditor
The manual and admin work
- Draft request lists, the RCM and the audit program
- Check uploaded evidence and flag AI-generated documents
- Test every sample and mark pass or fail on the evidence
- Analyze full populations and explain the anomalies
- Draft issues and report content
- Check the evidence that an issue is fixed
Your audit team
What humans do best
- Build relationships with stakeholders
- Apply judgment and business context to risk
- Prioritize the processes and exceptions that matter
- Expand audit coverage
- Deepen business knowledge and specialization
- Conclude on report ratings
30+AI use cases built in
With governance and security you can trust, backed by accountability.
From planning to issue closure, CoAuditor runs the whole audit and MJ works inside every phase.
1 / 6
Plan
Track external risk events relevant to your business for stronger risk-based planning.
2 / 6
RCM and program
MJ drafts the RCM and the audit program from your walkthrough notes.
3 / 6
Requests and evidence
Send PBC requests, track them, and confirm that what you received is what you asked for.
4 / 6
Testing
MJ tests every sample, shows the supporting passage, and analyzes the full population.
5 / 6
Reporting
MJ drafts findings and report sections from your results. Your team edits and concludes.
6 / 6
Issues and follow-up
MJ checks that management's fix addresses the action plan before you close the issue.
Between audits, CoAuditor keeps watching.
Continuous monitoring of your controls, on a schedule or as new data arrives.
 You asked, MJ built the checkFlag any invoice paid twice.
- SAP
- Oracle Fusion
- NetSuite
- PeopleSoft
- JD Edwards
- Any API or webhook
 CoAuditor
- Duplicate payments
Exception: the same invoice was paid twice.
Sent to your team to review
- Segregation of duties
- Payment thresholds
- SAP
- Oracle Fusion
- NetSuite
- PeopleSoft
- JD Edwards
- Any API or webhook
- Duplicate payments
Exception: the same invoice was paid twice.
Sent to your team to review
- Segregation of duties
- Payment thresholds
Connect
SAP, Oracle Fusion, NetSuite, PeopleSoft, JD Edwards, or any system with an API or webhook.
Monitor
Built-in rules for thresholds, duplicates and segregation of duties, or describe a check in plain language and MJ builds it.
Act
Each exception shows why it was flagged, so your team can review it and decide what it means.
See it in the product
How internal audit keeps pace with AI-era risk
Three minutes on the questions boards are asking, and how MJ and your auditors answer them: from planning to testing to monitoring between audits.
One third-party risk audit. 235 hours became 14.
13 key controls, an average of 5 test steps per control, 195 PBCs.
- Audit program28hto2h
- PBC sorting13hto6h
- Operating effectiveness testing182hto3h
- Audit report, first draft8hto2h
- Grammar and punctuation corrections4hto1h
Your evidence stays yours.
Security, governance and accountability are built into every audit and every AI result.
SOC 2 Type II
Our controls are independently attested to SOC 2 Type II.
Your data never trains AI
We do not train AI models on your data, and our AI providers do not either.
Your data stays in your region
Data residency, encrypted storage and data isolation for every client.
Every AI result is accountable
A panel of AI reviewers and a judge check each test, every result shows its evidence, and your team reviews and approves it. Every action is in the audit trail.
- Single sign-on and fine-grained access
- GDPR best practices
- CISA Secure by Design pledge
- Patent pending
We don't do everything. We do internal audit.
Built for internal audit teams, on purpose. Focus is how we do it well.
- Finance
- Risk
- Compliance
- Internal audit
- IT
- ESG
- Legal
Already have a GRC?
Add CoAuditor beside it to close the intelligence and automation gap most GRC platforms leave.
Your team.At the speed of risk.
See MJ work on your own audit in 30 minutes.
Book a demo
ROI calculator. Fast, private, on-page results.
How much time and budget can you win back?
Get a tailored ROI estimate for your whole audit lifecycle, from risk and control matrices to issue management.
- Six quick questions, under a minute
- Built from your own audit volume and costs
- A board-ready PDF report to download
Make the business case
Secure and private
Frequently asked questions
Still have questions? Contact us or .
How many samples can CoAuditor test? Do we have to test everything?
You decide, control by control. CoAuditor's automation supports both sample testing and full population testing, so you can test the sample your methodology calls for, or the whole population where volume or risk makes a sample a weak answer.
How long does implementation take?
Implementation takes 3 to 6 weeks, depending on the scope of your rollout.
Can we import our existing RCM and issues into CoAuditor?
Yes. You can bring your existing risk and control matrix and your open issues into CoAuditor, so you start from your own methodology and history, not a blank page.
Can we try CoAuditor before we commit?
Yes. We offer a trial of up to one month on a real audit. If you would rather not use live data, we provide work papers for you to test with.
What training and support do we get?
Onboarding includes dedicated support and training sessions for your team. CoAuditor also has built-in video tutorials and reading material, available from each auditor's account, for continued learning.
How is our data handled?
Your data is never used to train AI models, by us or by our AI providers. It is encrypted, isolated for each client and protected by fine-grained access controls, and our controls are independently attested to SOC 2 Type II.
Where is our data hosted?
Your data resides where you direct us to host it, in the country or region you choose.
Do you support SSO (Okta, Azure AD, etc.)?
Yes. Single sign-on is supported. Admins can enforce login policies (SSO, SAML, OIDC) and manage roles and permissions centrally.